Triage: you don't need to review alerts one by one
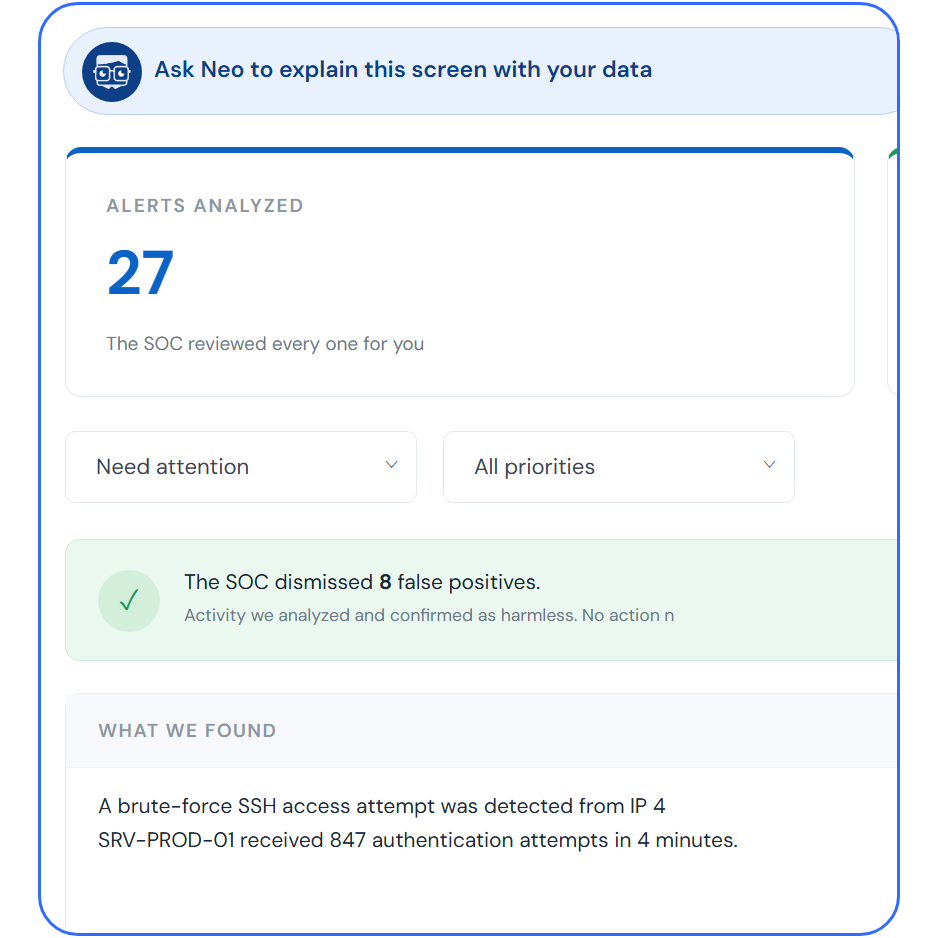
IT gets thousands of alerts a day and most are false alarms. An agent reviews every one the moment it appears and leaves you only the ones you actually need to see.
Agentic SOC for IT teams buried in thousands of alerts and false positives. On the Response and Compliance plans, human analysts are always on duty.
8+ years protecting companies across industries
We connect your systems and switch on monitoring. From then on, our agents watch them all year round.
In the meeting after an incident, everyone looks at your team before any other department.
Your client learns their data was at risk, and the relationship ends there.
An auditor asks for logs, and you have to pull them device by device and then put them in order.
One console per tool, and someone on your team collecting screenshots for the weekly report.
An agentic SOC that never blinks
IT gets thousands of alerts a day and most are false alarms. An agent reviews every one the moment it appears and leaves you only the ones you actually need to see.
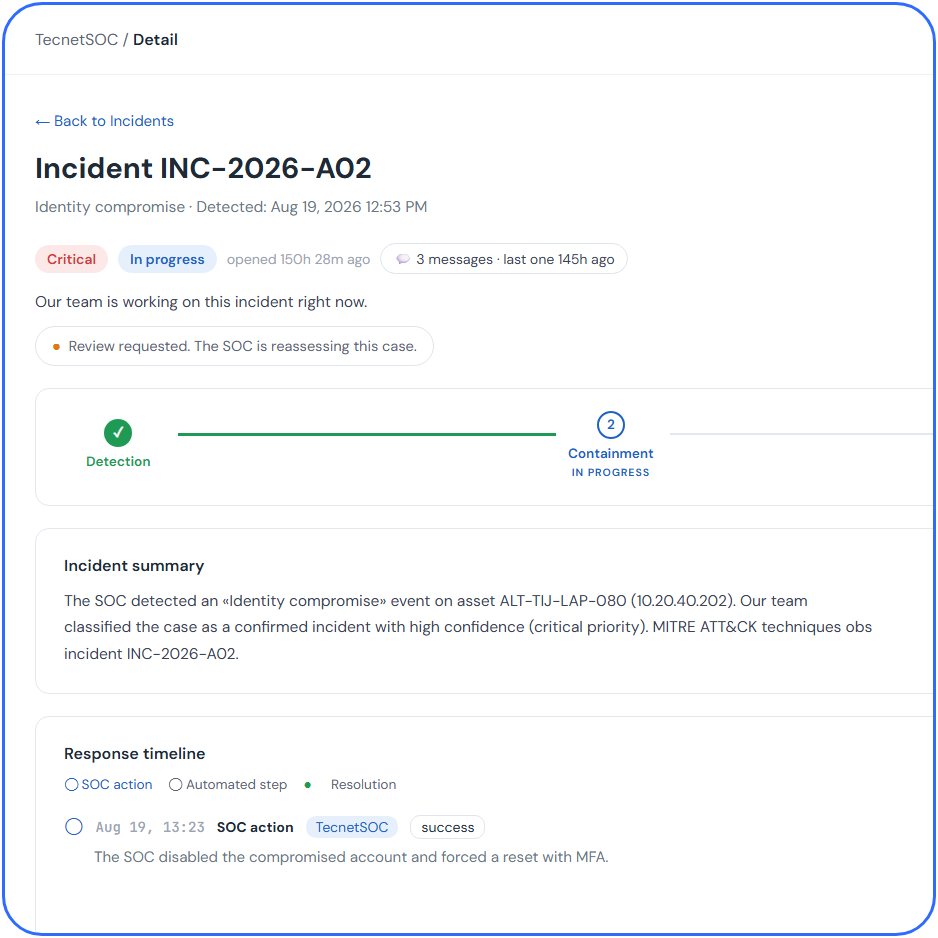
An analyst used to open a stack of different screens to understand what happened: who got in, from where and what they touched. Now we bring those pieces together in a single view.
When a threat is confirmed, we prepare the response and carry out the low-risk steps right away. Anything critical, we decide together with your team.
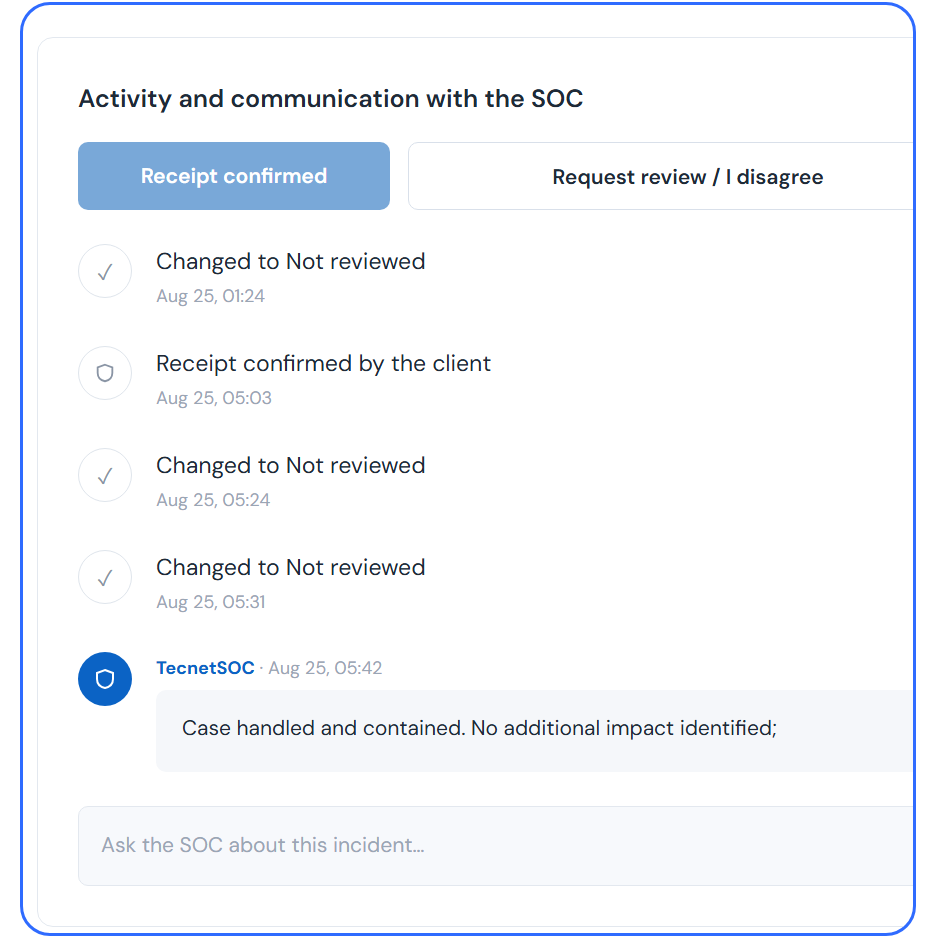
We log every action the moment it happens. When your auditor arrives, there's no file to assemble at the last minute because it's already done.
Hi, I'm Neo
Your AI analyst on call inside TecnetSOC
Ask it to investigate a device, a user or a signal, and it opens the case like an analyst on shift, walking you through a verdict step by step.
It also acts when you ask, from running a backup to quarantining a suspicious email. It can even run a disaster recovery drill.
Ask what the data on your TecnetSOC screen means and it answers with context. One click builds the executive summary.
Continuous SOC monitoring across every critical asset
From what your company exposes on the internet to the device that needs isolating mid-morning
Continuous monitoring of your network and endpoints, without anyone on your side covering shifts.
Every alert is investigated, correlated against the MITRE ATT&CK framework and enriched with threat intelligence before it reaches an analyst.
Every case logged from start to finish.
We watch the availability and performance of your network, apps and infrastructure, beyond security threats.
A full inventory of your network: servers, devices and installed software. You know what you have and what still needs protection.
We deploy critical updates before a known vulnerability becomes the way in.
Detection and containment on every device, always with your approval before isolating critical incidents.
We find vulnerabilities and rank what to patch first by real risk.
Continuous monitoring of what your company exposes, before someone else exploits it.
Phishing and business email compromise filtering before anything reaches your users' inboxes.
Phishing simulations and ongoing training for your users, so the human link isn't the weakest one.
Evidence and executive reports sent to the roles you define in the portal, ready for leadership.
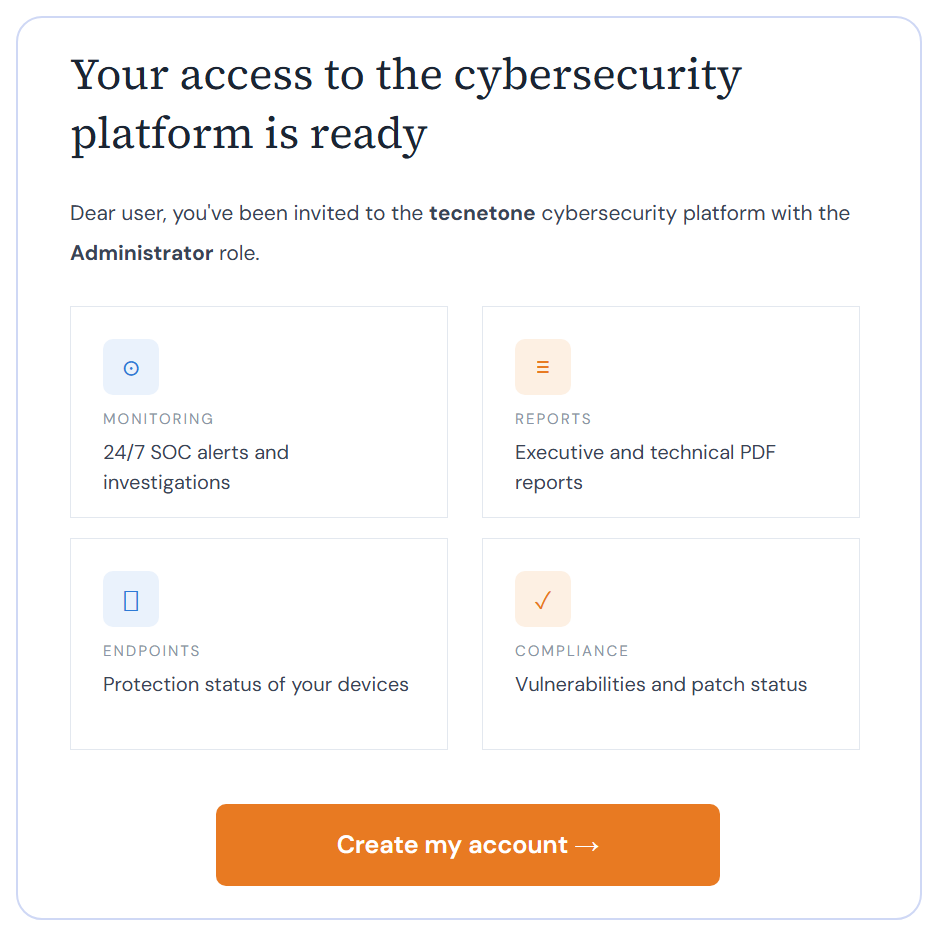
A member of the TecnetSOC team sets up your account with Microsoft SSO or email and password. When you log in, a getting-started guide walks you step by step through what to do to start seeing real data.
This is the most important step: download and install the TecnetSOC agent for your operating system (Windows, macOS DMG/PKG or Linux DEB/RPM). No extra manual setup and no endless meetings for your IT team.
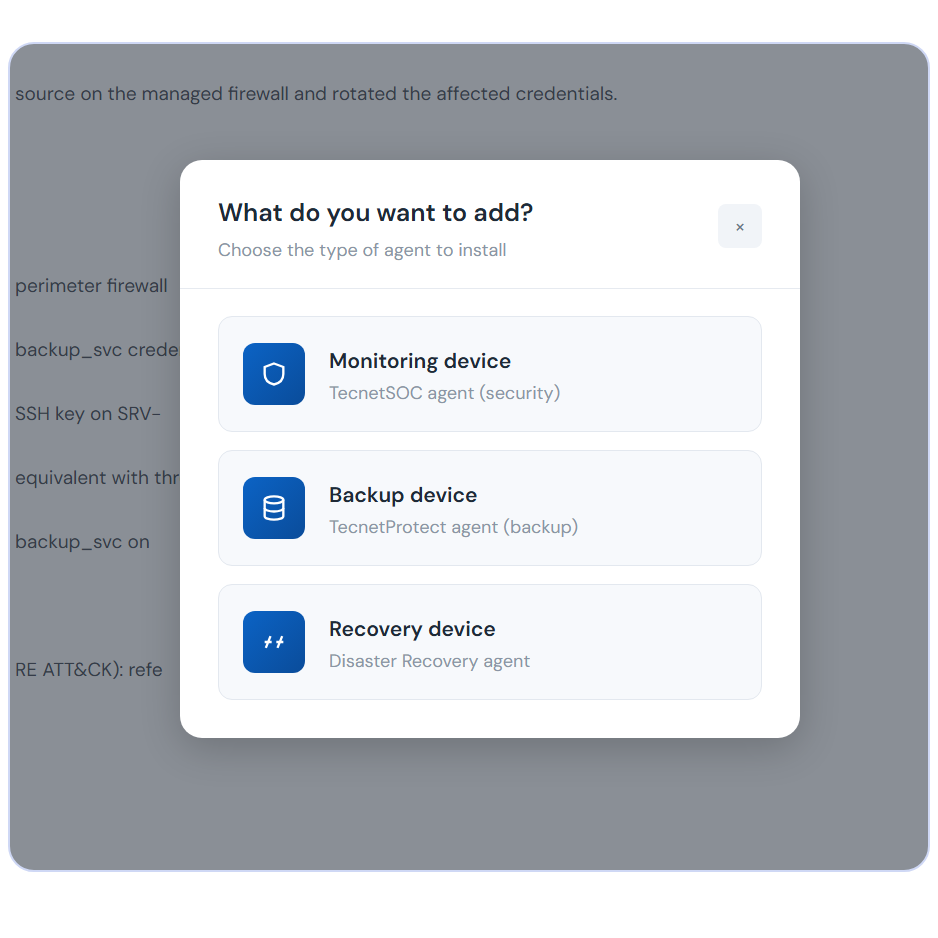
The TecnetSOC agent automatically deploys everything your plan includes so you start getting real data. There's nothing else you need to do.
Traditional SOC or agentic SOC: how to compare managed SOC providers
| Factor | Traditional SOC | TecnetSOC (agentic SOC) |
|---|---|---|
| Alerts |
Traditional SOC
Thousands of unfiltered alerts. Your analyst decides what to look at, blind. |
TecnetSOC (agentic SOC)
We prioritize every alert in seconds with autonomous triage, filtering out the low-risk ones before they reach a person. |
| Notification |
Traditional SOC
You depend on the vendor's support or your internal team, and nobody tells you when your alert actually starts being handled or how long it will take. |
TecnetSOC (agentic SOC)
Your alert goes into investigation in seconds with no queue, and when a case is confirmed critical our team steps in to make decisions with you or follow the playbook. |
| Coverage |
Traditional SOC
Covering every hour with your own staff means rotating shifts, burnout and turnover on your team. |
TecnetSOC (agentic SOC)
AI agents never stop, and on the Response and Compliance plans our own analysts staff the SOC continuously. Your team stops putting out fires and keeps its focus on what matters. |
| Your tools |
Traditional SOC
One console for antivirus, another for the firewall, another for email, and each one swears everything is fine. |
TecnetSOC (agentic SOC)
We integrate with more than 40 tools your company already uses, so you can see everything from a single platform. |
| The audit |
Traditional SOC
Compliance evidence assembled by hand the night before the audit: screenshots, conversations, files and emails someone has to track down one by one. |
TecnetSOC (agentic SOC)
Everything is recorded in the platform, so your team members automatically receive weekly, monthly, quarterly and annual reports based on their role. |
| What you pay |
Traditional SOC
The SOC is sold in pieces: agents, artificial intelligence and integrations are quoted separately, or you have to bring them yourself. |
TecnetSOC (agentic SOC)
One per-device subscription that already includes the agents, the AI and more than 40 integrations. Choose your plan and everything works. |
Priced per device from 19 USD a month, with a free plan for up to 10 devices. Agents, AI and integrations included.
Need backup, DLP or anti-spam? . Add-ons can be set up on any plan.
Why TecnetOne?
We operate under the same standards we help you meet.
Our own team answers 9:00 a.m. to 6:00 p.m. Central Time (CT), Monday through Sunday.
The team that responds when something happens is the same one that knows your operation every day.
You always see the record of what we're doing, not a generic "all good."
The standards behind our work
How TecnetOne has backed companies like yours
"TecnetOne's incident response was exactly what you'd expect from a top-tier provider: fast, precise, and without our team having to explain the situation twice. Their managed monitoring and protection services gave us visibility where we had none before. Now we have a team that detects, alerts us, and acts before a risk becomes a bigger problem."
"Beyond their strength in the cloud, their cybersecurity work has served as a built-in layer of protection, not an add-on. Knowing our environments are monitored and safeguarded by the same team that manages them gives us an operational consistency we really value."
"TecnetOne's expertise in managing cloud services is impressive. They helped us implement and maintain our infrastructure efficiently. Through their managed services, we get security recommendations and best practices to protect the critical environments our operations depend on. TecnetOne is a partner we trust."
"From our very first conversation, the TecnetOne team showed deep knowledge of security and a strong commitment to service, always in line with industry standards. Whenever a risk comes up, they're on top of it and put best practices in place to mitigate it."
SOC as a Service (SOCaaS) is a SOC (security operations center) delivered as a managed service: the team that watches a company's cybersecurity around the clock.
In an agentic SOC, AI agents triage alerts, correlate events and run the first investigation, while human analysts supervise and decide the critical cases. Unlike traditional automation, the agent reasons through each case instead of following a fixed script.
No. The agents investigate, correlate evidence and carry out predefined low-risk containment actions. Critical decisions, such as isolating a server or notifying a client, are always approved by a human analyst.
Either way, yes. TecnetSOC serves mid-size and large enterprises, as well as smaller companies that need a security operations center without building one in-house. If you have an IT team, the disciplines are different: IT keeps operations and projects running, while the SOC watches for threats all day. We detect and respond, and your team only gets what needs its decision. If you have no security department, we become that department, so you don't need to hire anyone to start. Our support team is available 9:00 a.m. to 6:00 p.m. Central Time (CT), Monday through Sunday, in English and Spanish. Our incident response line is always open to any company facing a security incident, whether or not it is a TecnetSOC customer. On the Response and Compliance plans, our SOC analysts also monitor and respond continuously.
No. Monitoring works on activity logs and behavior patterns; the content of your files, emails and conversations stays out of scope. We process only what's needed to detect anomalies, under ISO 27001 controls, and the exact scope is written into your contract.
If you decide not to buy, your account automatically moves to the Visibility plan, which is free for up to 10 devices and renews every year. You don't have to reinstall anything or reconfigure the agents.
MDR (managed detection and response) focuses on detecting and responding to threats, mostly on endpoints. SOC as a Service covers the whole security operations center: continuous monitoring across endpoints, identity, network and cloud, investigation, incident management and compliance reporting. TecnetSOC's Response and Compliance plans include managed detection and response across endpoints, email and identity: AI agents investigate and contain each threat, while TecnetOne's own analysts in Latin America, working in three shifts, supervise continuously and prioritize every incident by severity.
Not as part of the plans. TecnetOne offers proactive threat hunting, the search for threats that have not yet triggered an alert, as a customized additional service, with its scope defined with each customer and quoted separately.
TecnetSOC is priced per device per month in USD. Visibility is free for up to 10 devices; Guard starts at $19, Response at $27 and Compliance at $37 per device per month, or $17, $24 and $34 with annual billing. You can try Response free for 30 days. The price already includes the agents, artificial intelligence and more than 40 integrations; they are not billed separately. Services are quoted and invoiced in US dollars by TecnetOne LLC, based in the United States.
Yes. TecnetSOC includes SIEM: it correlates events from your computers, servers, cloud and identities against the MITRE ATT&CK framework, and our AI agents and analysts investigate every alert around the clock. It also includes vulnerability management on every plan: continuous CVE analysis on computers and servers, with CVSS severity. From the Guard plan up, patch deployment is added, prioritized by real exploitation risk (CISA's KEV catalog and EPSS probability) and with closure verification. You don't need to license a separate SIEM: the TecnetSOC agent deploys it based on your plan. If you need a one-time assessment with a report and a results session, see our vulnerability assessment.
Yes. TecnetOne is ISO/IEC 27001 certified, the international standard for information security management. That means our own operation, including the SOC that monitors our clients, runs under an information security management system audited by a third party. With TecnetSOC we also help clients prepare for their own certification: the Compliance plan enables TecnetGRC, the platform to manage risks, controls, evidence and the auditor's document room.
Before you hire a traditional SOC or start from scratch, try ours
TecnetSOC pairs AI agents that investigate every alert in seconds with analysts who decide what to do about it.