Triage: you don't need to review alerts one by one
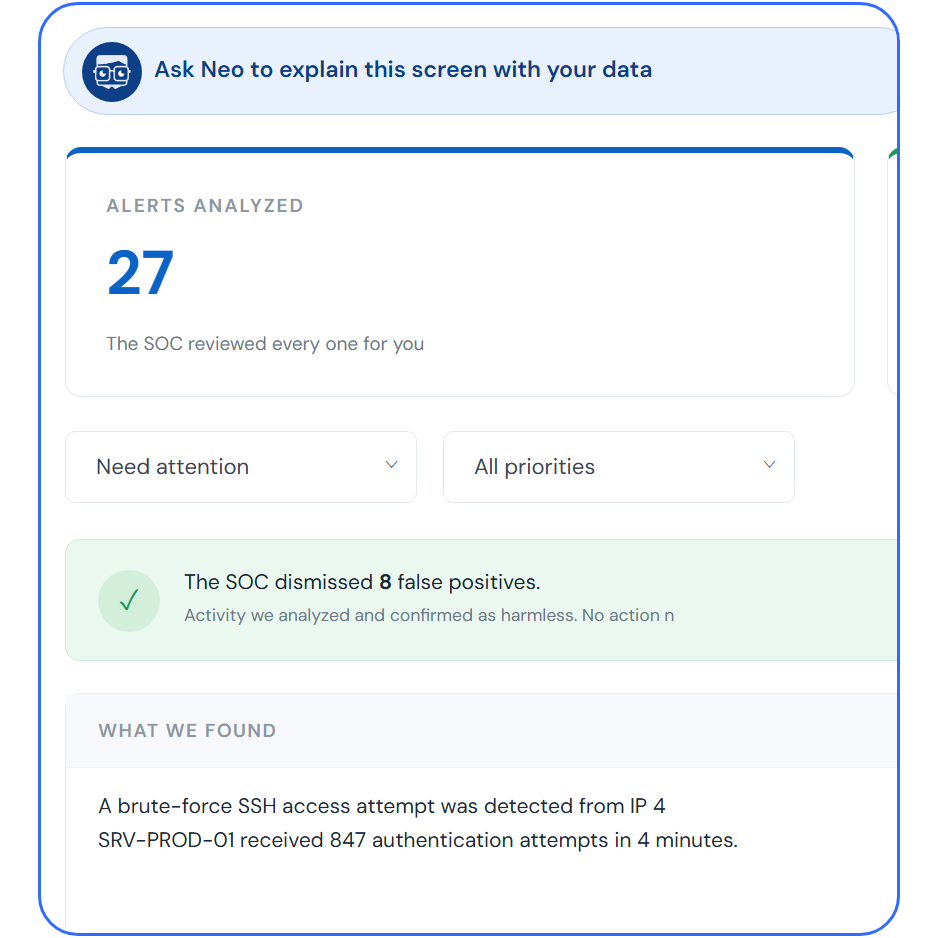
IT gets thousands of alerts a day and most are false alarms. An agent reviews every one the moment it appears and leaves you only the ones you actually need to see.
Agentic SOC 24/7 for IT teams buried in thousands of alerts and false positives.
8+ years protecting companies across industries
We connect your systems and switch on monitoring. From then on, our agents watch them all year round.
In the meeting after an incident, everyone looks at your team before any other department.
Your client learns their data was at risk, and the relationship ends there.
An auditor asks for logs, and you have to pull them device by device and then put them in order.
One console per tool, and someone on your team collecting screenshots for the weekly report.
An agentic SOC that never blinks
IT gets thousands of alerts a day and most are false alarms. An agent reviews every one the moment it appears and leaves you only the ones you actually need to see.
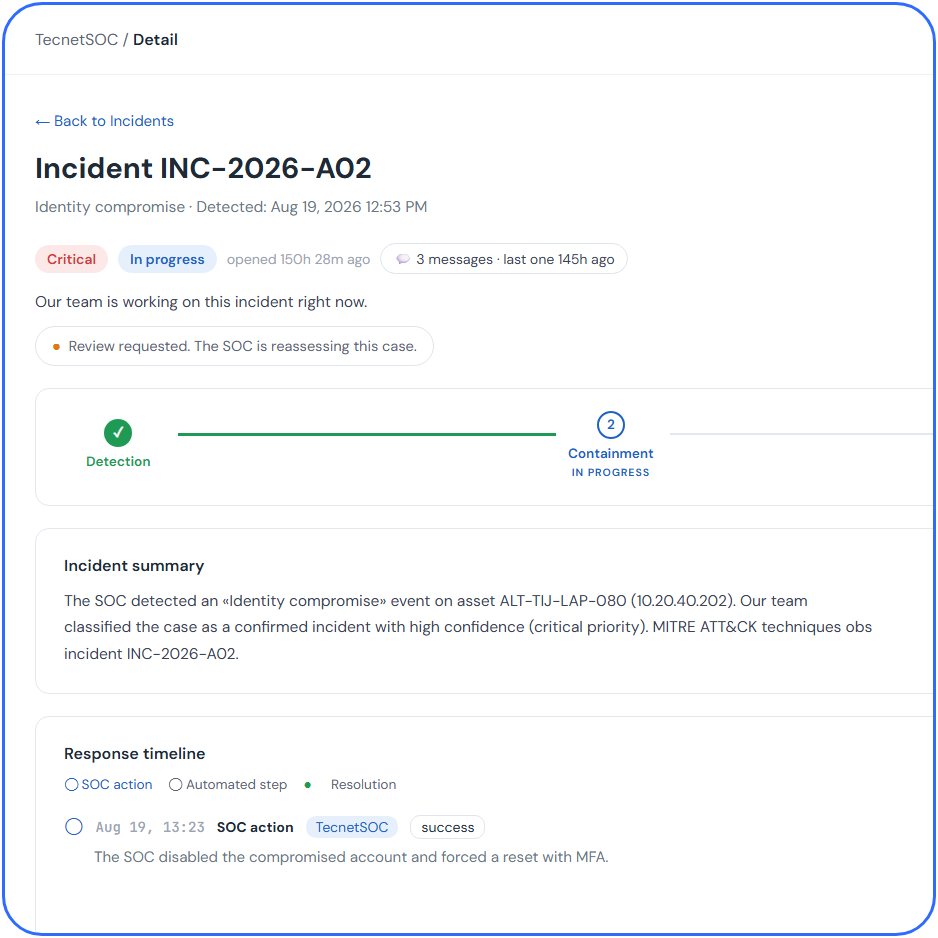
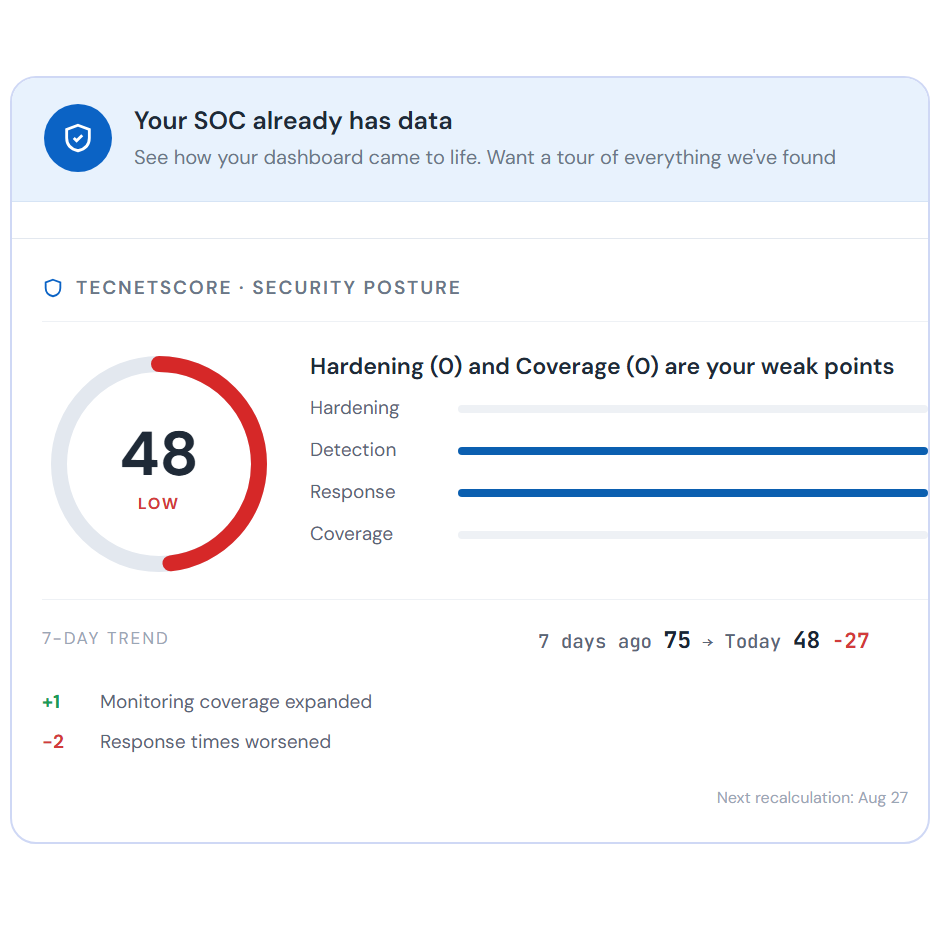
An analyst used to open a stack of different screens to understand what happened: who got in, from where and what they touched. Now we bring those pieces together in a single view.
When a threat is confirmed, we prepare the response and carry out the low-risk steps right away. Anything critical, we decide together with your team.
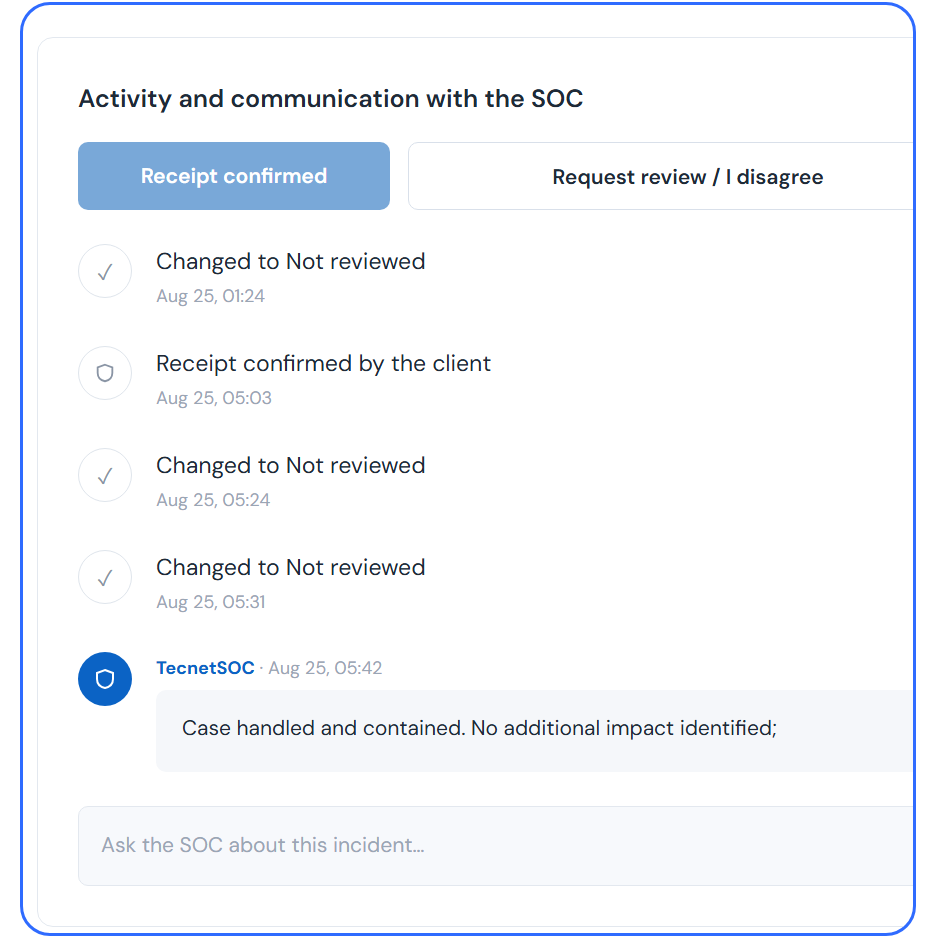
We log every action the moment it happens. When your auditor arrives, there's no file to assemble at the last minute because it's already done.
Hi, I'm Neo
Your AI analyst on call inside TecnetSOC
Ask it to investigate a device, a user or a signal, and it opens the case like an analyst on shift, walking you through a verdict step by step.
It also acts when you ask, from running a backup to quarantining a suspicious email. It can even run a disaster recovery drill.
Ask what the data on your TecnetSOC screen means and it answers with context. One click builds the executive summary.
24/7 SOC monitoring across every critical asset
From what your company exposes on the internet to the device that needs isolating mid-morning
We watch the availability and performance of your network, apps and infrastructure, beyond security threats.
A full inventory of your network: servers, devices and installed software. You know what you have and what still needs protection.
We deploy critical updates before a known vulnerability becomes the way in.
Detection and containment on every device, always with your approval before isolating critical incidents.
We find vulnerabilities and rank what to patch first by real risk.
Continuous monitoring of what your company exposes, before someone else exploits it.
Phishing and business email compromise filtering before anything reaches your users' inboxes.
Phishing simulations and ongoing training for your users, so the human link isn't the weakest one.
Evidence and executive reports sent to the roles you define in the portal, ready for leadership.
A member of the TecnetSOC team sets up your account with Microsoft SSO or email and password. When you log in, a getting-started guide walks you step by step through what to do to start seeing real data.
This is the most important step: download and install the TecnetSOC agent for your operating system (Windows, macOS DMG/PKG or Linux DEB/RPM). No extra manual setup and no endless meetings for your IT team.
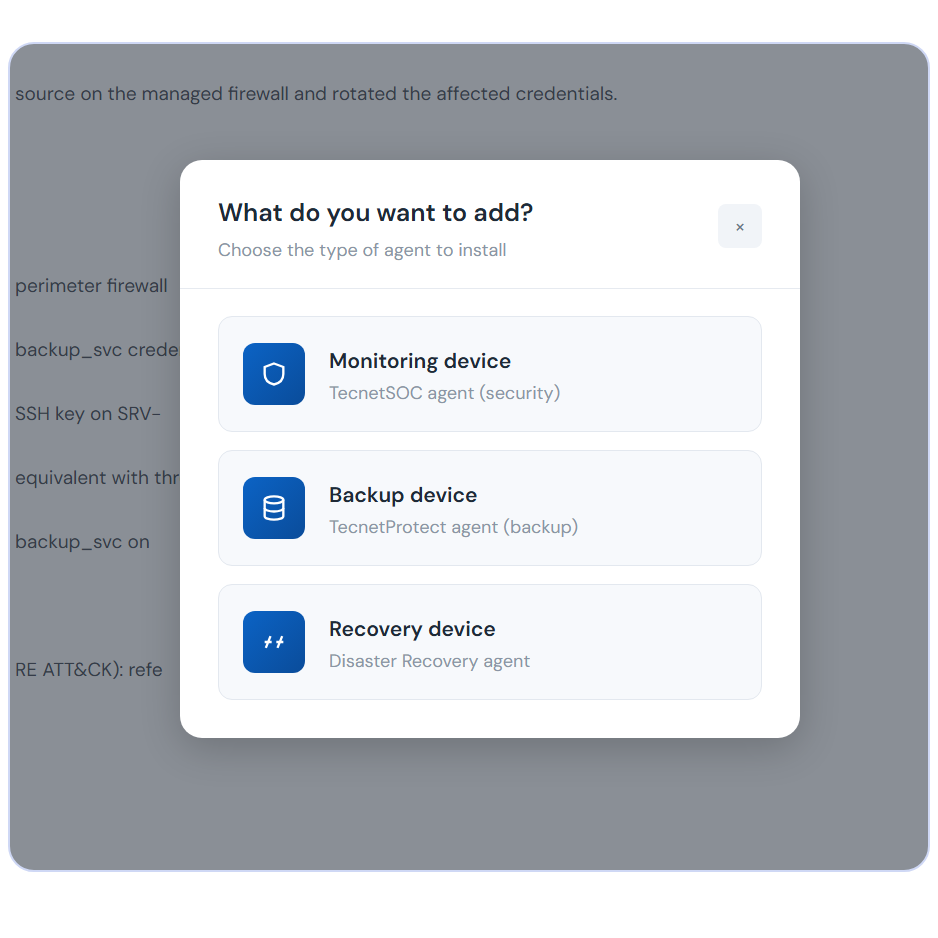
The TecnetSOC agent automatically deploys everything your plan includes so you start getting real data. There's nothing else you need to do.
Traditional SOC or agentic SOC: how to compare managed SOC providers
| Factor | Traditional SOC | TecnetSOC (agentic SOC) |
|---|---|---|
| Alerts |
Traditional SOC
Thousands of unfiltered alerts. Your analyst decides what to look at, blind. |
TecnetSOC (agentic SOC)
We prioritize every alert in seconds with autonomous triage, filtering out the low-risk ones before they reach a person. |
| Notification |
Traditional SOC
You depend on the vendor's support or your internal team, and nobody tells you when your alert actually starts being handled or how long it will take. |
TecnetSOC (agentic SOC)
Your alert goes into investigation in seconds with no queue, and when a case is confirmed critical our team steps in to make decisions with you or follow the playbook. |
| Coverage |
Traditional SOC
24/7 coverage means rotating shifts, team burnout and staff turnover. |
TecnetSOC (agentic SOC)
We cover your operation 24/7 with active agents, so your team stops putting out fires and keeps its focus on what matters. |
| Your tools |
Traditional SOC
One console for antivirus, another for the firewall, another for email, and each one swears everything is fine. |
TecnetSOC (agentic SOC)
We connect all your tools to each other in the platform and alert you once, when it's truly critical. |
| The audit |
Traditional SOC
Compliance evidence assembled by hand the night before the audit: screenshots, conversations, files and emails someone has to track down one by one. |
TecnetSOC (agentic SOC)
Everything is recorded in the platform, so your team members automatically receive weekly, monthly, quarterly and annual reports based on their role. |
Priced per device. No infrastructure of your own required.
Need backup, DLP or anti-spam? . Add-ons can be set up on any plan.
Why TecnetOne?
We operate under the same standards we help you meet.
Our own support team responds based on the severity of each case, with coverage during US business hours.
The team that responds when something happens is the same one that knows your operation every day.
You always see the record of what we're doing, not a generic "all good."
“It is a long established fact that a reader will be distracted by the readable content of a page when looking at its layout.”
How TecnetOne has backed companies like yours
( 5 )
"TecnetOne's experience managing cloud services is impressive. They helped us implement and maintain our infrastructure efficiently."
( 5 )
"Their response was what you expect from a top-tier provider: fast, precise, and without having to explain twice what was going on. It's the kind of provider you want to have identified before you need one."
( 5 )
"Our cloud infrastructure has been in TecnetOne's hands for several years. Their team knows our environment inside out, so every change, scale-up or incident gets handled."
( 5 )
"Their team understands our environment and knows how we operate. They always bring recommendations, and their expertise shows in the quality of the service every day."
SOC as a Service (SOCaaS) is a SOC (security operations center) delivered as a managed service: the team that watches a company's cybersecurity around the clock.
In an agentic SOC, AI agents triage alerts, correlate events and run the first investigation, while human analysts supervise and decide the critical cases. Unlike traditional automation, the agent reasons through each case instead of following a fixed script.
No. The agents investigate, correlate evidence and carry out predefined low-risk containment actions. Critical decisions, such as isolating a server or notifying a client, are always approved by a human analyst.
Either way, yes. If you have an IT team, the disciplines are different: IT keeps operations and projects running, while the SOC watches for threats all day. We detect and respond, and your team only gets what needs its decision. If you have no security department, we become that department, so you don't need to hire anyone to start. Our support team covers US business hours in English and Spanish.
No. Monitoring works on activity logs and behavior patterns; the content of your files, emails and conversations stays out of scope. We process only what's needed to detect anomalies, under ISO 27001 controls, and the exact scope is written into your contract.
If you decide not to buy, your account automatically moves to the Visibility plan, which is free for up to 10 devices and renews every year. You don't have to reinstall anything or reconfigure the agents.
The standards behind our work
Before you hire a traditional SOC or start from scratch, try ours
TecnetSOC pairs AI agents that investigate every alert in seconds with analysts who decide what to do about it.