
Frequently asked questions
A cybersecurity company in the United States protects other organizations' systems and data: it monitors them around the clock and tests their defenses with controlled attacks. At TecnetOne, an agentic SOC watches your operation day and night and our penetration testing finds the gaps before an attacker does. We also help you gather year-round the evidence that SOC 2, PCI DSS and your customers ask for.
Public companies must file Form 8-K, Item 1.05, within four business days after determining that a cybersecurity incident is material. They also have to describe how they manage cybersecurity risk every year in Form 10-K. We help you detect incidents early and keep the evidence ready to assess them within that deadline.
No law requires it, but many customers ask for a SOC 2 report before they sign a contract, especially if you store or process their data. Getting there means having documented controls and proof that they work. We prepare you for the audit with TecnetGRC gap assessments, and our 24/7 monitoring builds that evidence all year.
Ask who watches your devices overnight and whether that work is outsourced, whether the provider holds ISO/IEC 27001 certification and how well it knows SOC 2, PCI DSS and SEC rules. Request a sample report: every alert should come with evidence and the action taken, ready for an auditor or a customer review. Pricing should be clear from the first conversation.
Most small and midsize businesses don't have security analysts on call overnight, and a managed service fills that gap without building an internal team. It also gives you the evidence to answer the security questionnaires larger customers send. At TecnetOne we price monitoring per device, so the cost tracks the size of your operation.
Yes. Monitoring runs remotely: you install an agent on each device and we watch it 24/7, with no on-site visits or extra hardware. Penetration testing and compliance work are also done remotely, with meetings scheduled in your time zone and reports you can share with leadership or an auditor.
TecnetSOC Agentic 24/7 monitoring costs USD 19 to 37 per device per month, depending on the plan you choose. You can try it for 30 days before you decide: install the agent on your devices and see how we investigate each alert and what evidence comes in every report. See the plans on our TecnetSOC Agentic page.
TecnetSOC Agentic plugs into what you already run: your antivirus, firewall, email and cloud stay as they are, with 40+ integrations, and if one is missing we evaluate it. From the Guard plan up, SIEM, EDR/XDR, RMM, vulnerability management and asset inventory are included, with unlimited EPS and storage: you pay per device. AI agents work every detection 24/7, investigate it and respond, our team approves critical actions, and the operation is 200X more efficient than a traditional SOC.
The latest in cybersecurity, explained by our team
Guides, analysis and trends to keep your IT team one step ahead.
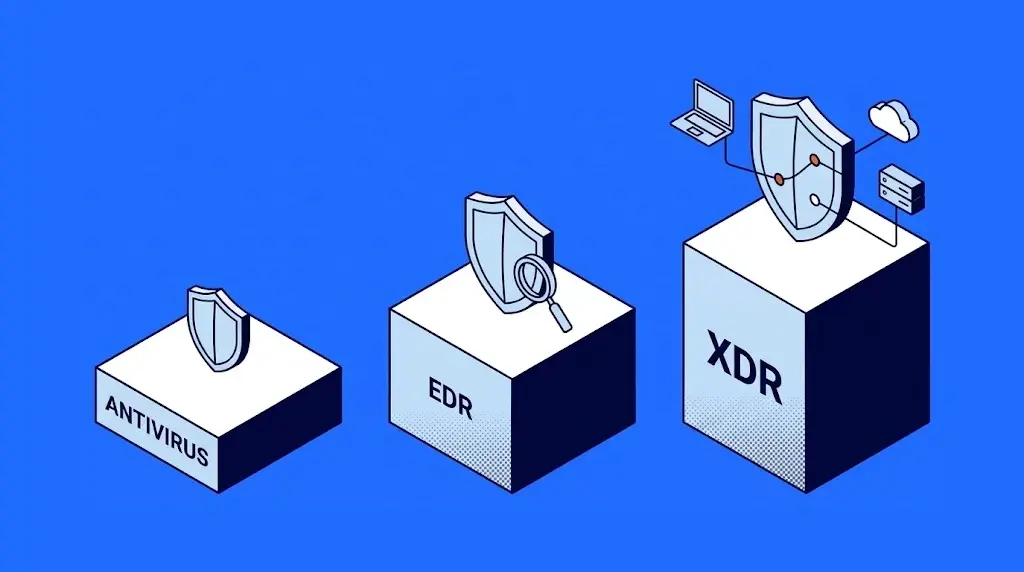
EDR vs Antivirus vs XDR: What Each One Is and Which One You Need
EDR watches how your devices behave; antivirus blocks known threats and XDR correlates every source. How they differ and which one fits your company.
Read more
How Much Does a SOC Cost? SOC as a Service Pricing Explained
SOC as a service pricing usually runs 10 to 50 USD per device per month. What the price includes, pricing models and how to compare managed SOC …
Read more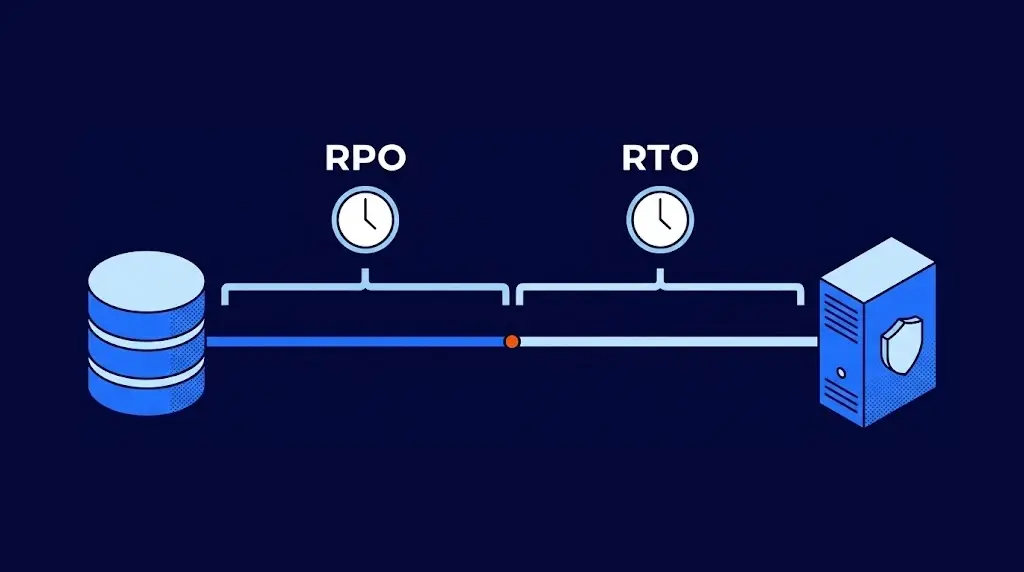
RTO vs RPO Explained with Examples: How to Set Them in Your Company
RTO is how long a system can be down; RPO is how much data you can afford to lose. Key differences, examples by system and how to calculate them.
Read more