More and more security work happens inside a conversation with an agent. The question that matters to whoever runs IT is a different one: can I trust it to take action on my company's infrastructure? Agentic cybersecurity answers with an operating model in which AI agents investigate and act, and a person makes the critical calls (human in the loop).
Agent-driven workflows have made it faster than ever to go from alert to decision. But in security, the margin for error is razor thin: when an agent acts on a device, the effect reaches your entire operation.
Most tools force you to choose between speed, control, and evidence. Over time, that choice turns into thousands of unread alerts, one console per tool, and reports pieced together by hand the night before every audit. According to the State of the SOC study by Microsoft and Omdia, the average organization uses 10.9 security consoles, 46% of its alerts are false positives, and 42% are never investigated.

Attackers are already using AI. In its Cost of a Data Breach 2026 study, IBM reports that 1 in 4 malicious breaches involved AI, up 56% from the previous year, mostly through deepfake impersonation and AI-assisted malware. Launching an attack keeps getting faster and cheaper, and at that speed, defenders need AI agents on their side too. Organizations that reported using AI and automation in their security operations cut the cost of a breach by nearly USD 2 million on average.
The teams that win in the agentic era will run on a platform that balances the speed of AI with the control and evidence needed to trust agents with high-impact work. At TecnetOne, we built that platform.
Introducing Neo and TecnetSOC Agentic
Today, TecnetOne introduces Neo, the AI orchestrator and on-call analyst, and TecnetSOC Agentic. What we announced piece by piece now comes together in one place, with control and evidence for every action.
A complete security team. It's called TecnetSOC.
TecnetSOC is TecnetOne's MDR (managed detection and response) service, run by an agentic SOC: a human team and AI agents detect, investigate, and respond to incidents in your company. It's the agentic cybersecurity platform ready to work alongside your IT team, and critical decisions are made together with a person.
Three things set it apart from other traditional SOCs (MDR):
- Vendor-agnostic, built on what you already have. We connect your antivirus, firewall, email, and cloud as they are, and everything keeps working just like today.
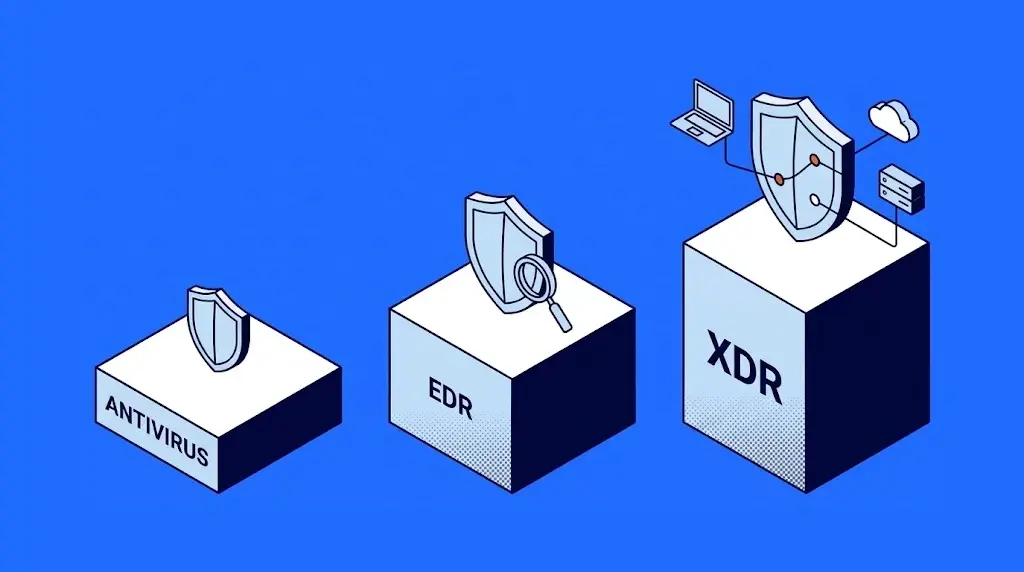
- Complete, all in one platform. Event correlation (SIEM), endpoint protection (EDR/XDR), remote management (RMM), vulnerability management, and inventory all come included in the same portal starting with the Guard plan.
- Agentic, with AI at its core. Multiple AI agents work together on every case and recommend an action to your team, along with the evidence behind it.

Neo started out answering in read-only mode, using your account information with the source in plain view. Next, it was built into every screen of the portal to explain what you're looking at using your own data, and later it gained the ability to take action, always with prior confirmation and a record of who authorized each one. Today it investigates and acts with your approval, on a platform that already brings together every piece of your security operation. Each stage is covered in the TecnetSOC updates.
"The response was exactly what you expect from a top-tier provider: fast, precise, and without having to explain twice what was going on."
Eduardo G., CEO, Logistics
Agentic cybersecurity with a human in the loop
In a traditional SOC, everything falls on people. In TecnetSOC Agentic, the agents do the work and your team makes the decisions.

- L1, monitoring and triage. The agents rule out false alarms and correlate signals in seconds.
- L2, investigation and response. The agents investigate and recommend an action, and your team approves it.
- L3, proactive threat hunting with Neo. Neo investigates the case and reports on it in business terms.
In our operation, TecnetSOC Agentic is 200 times more efficient than a traditional SOC, and 9 in 10 cases that warrant a closer look are false positives the system has already filtered out. That way, your company grows without adding more people dedicated to alerts. The agents take on the review and correlation, manual work that takes hours or even days, and your team brings the judgment.
Your IT team keeps you secure, and TecnetSOC Agentic gives it the speed of AI
Thousands of alerts, and most of them are false alarms
An AI agent analyzes every alert the moment it arrives and shows you only the ones that need your attention. Everything it rules out is counted and available for you to review.

One console per tool, and someone gathering screenshots for the report
TecnetSOC Agentic integrates with the tools you already use without replacing what works, and the modules of your operation come together in a single portal. When you log in, you see your TecnetScore, your security posture from 0 to 100 by pillar, and what the TecnetSOC team did for you this month. We alert you only once, when something is truly critical. Your weekly, monthly, or quarterly report opens with an executive dashboard, no manual screenshots needed. Recommendations come from the recommendation engine.
From that same portal, you can also:
- Prioritize updates. Patching separates what's pending from what was attempted but didn't finish, with a device-by-device breakdown.
- Decide on a held email. You see why it was held, and your admin releases it or reports it as legitimate. If it already reached inboxes, they can also pull it back.
- Unify your inventory. Devices, peripherals, and cloud services, each with its owner and the regulations that apply to it, plus evidence by regulation ready for your audit.
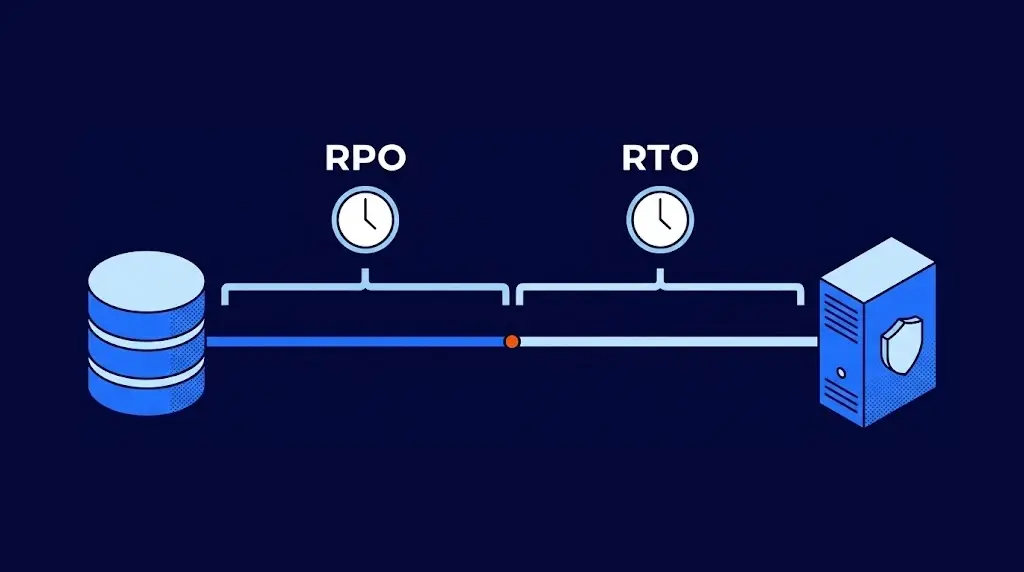
- Rehearse your recovery. With TecnetProtect Backup, you run a drill without disrupting your operation and keep a record of who ran it and how it went.

In the meeting after an incident, all eyes turn to your team
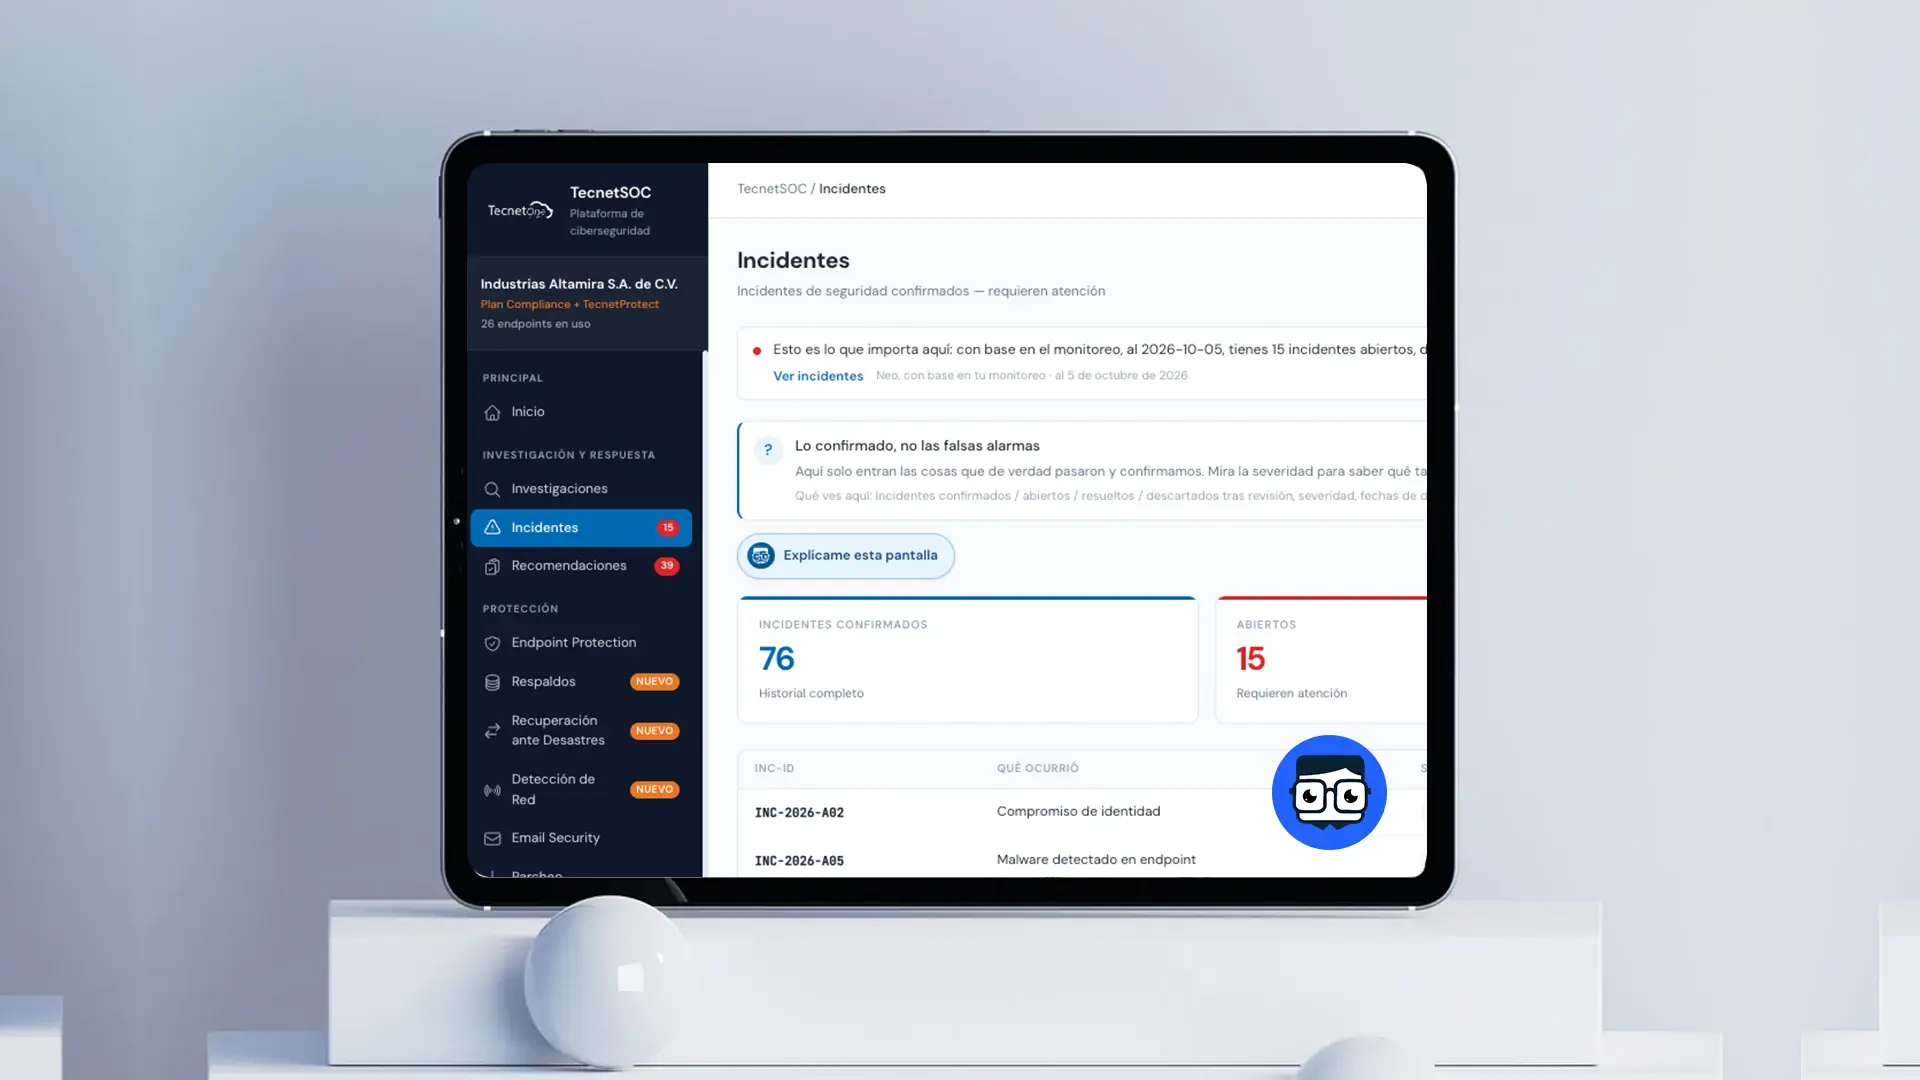
Every incident is a living case file with its stage timeline and a record of who did what, as we describe in the incidents module and the investigations module. If you disagree with a verdict, you request a review from the portal, and "Ask the SOC" opens the conversation right inside the case.

An auditor asks for logs, and someone has to collect them device by device
We log every action the moment it happens. The incident moves through stages, from detection to containment, eradication, and verification, and every step keeps its date and time. When your auditor arrives, the case file is already complete.

What your company exposes to the internet, and nobody sees
Attack Surface brings together your domains, exposed services, and expiring certificates, with a score and findings by severity. It tells you what to prioritize, although it doesn't replace a penetration test.

Now you can just ask Neo
- Ask it to investigate. Tell it which device, user, or signal you want to look into, and Neo opens the case and gives you a step-by-step verdict.
- Understand without translating. Ask it what something on your screen means, and it answers with your data. With one click, it generates the executive summary.
- Take action under your control. It checks which updates a device is missing or quarantines a suspicious email. Your admin authorizes with one click, and the result arrives in the chat even if you've closed the portal.

A real overnight case from 2026 with TecnetSOC Agentic
This real case from a TecnetSOC customer, shared here anonymized, was detected at 02:47 and closed before sunrise.

By the numbers: 3 alerts were consolidated into 1 single incident, 97 devices were reviewed that same night, and there was 0 business impact. The human team approved the closure, and the evidence was complete and ready to present. Afterward, Neo prepared the executive summary of the case for leadership, covering the risk it posed and what the TecnetSOC team resolved.
Collaborate securely at scale
As more people and more agents work on your security, you need clear rules, and TecnetSOC Agentic sets them from the portal.
- Neo proposes, your admin approves. Before it runs, every action waits for confirmation from whoever manages your account.
- You decide how each device is isolated. If the TecnetSOC team confirms an active threat, it can cut the device's network connection to stop the spread. While isolated, the device stays protected and monitored, and it gets its connection back when the team releases it. Device by device, you choose whether isolation is automatic or whether you'd rather we contact you first. Critical infrastructure devices are never isolated automatically.
- Roles and contacts you define. You assign your team's roles in the portal, with different access for the people who operate, audit, and lead. You decide which contacts we call when an incident requires it, and notifications go only to the people involved in each case.
- A complete activity log. Every action shows up with its time, its author, and its result, and the ones Neo runs are logged with who authorized them.
The platform for what comes next
Over time, agents will take on a larger share of the work of running your security. The organizations that come out ahead will be the ones with a platform built for it, with agents that propose, people who decide, and evidence for every step.
TecnetSOC Agentic is that platform, and it's designed so your team can lead security with instructions and approvals from a single portal. Agentic cybersecurity is the model, and an agentic SOC is how you run it, as we explain in our guide What is an agentic SOC?. SOAR-style automatic closure (orchestrated response with no intervention) remains on our roadmap.
Available today
Neo and every capability described here are already live in the portal, and each module is enabled based on your plan. If you're already a customer, log in to your portal: Neo is available on every screen. If you don't use TecnetSOC yet, try it for 30 days.
Frequently asked questions about agentic cybersecurity with TecnetSOC
"Agentic" describes an artificial intelligence system that takes action to achieve a goal, instead of just answering questions. In security, that means agents that investigate alerts and recommend actions, while a person makes the critical calls. The way to put it into practice is an agentic SOC.
Neo is TecnetSOC's AI orchestrator and on-call analyst. It's built into the portal, accessible from every screen, and answers using your own data. It investigates a device, a user, or a signal and explains what you're seeing without technical jargon. It only takes action when your admin authorizes it.
TecnetSOC Agentic brings together investigations and incidents, recommendations, endpoint protection, TecnetProtect backups, email security, patching, vulnerabilities, attack surface, security awareness, inventory, and reporting. Starting with the Guard plan, it includes SIEM, EDR/XDR, and RMM (event correlation, endpoint protection, and remote management), plus vulnerabilities and inventory, and access to the other modules depends on your plan.
In TecnetSOC Agentic, the agents investigate the case and recommend an action backed by correlated evidence. Critical decisions, such as escalating or closing an incident, are made together with a person. Neo's actions run only when whoever manages your account confirms them, and each one is logged with its time and author.
TecnetSOC integrates with what you already have, because we're not looking to replace what works. It includes its own SIEM, EDR/XDR, and RMM, and if you already use other tools, we connect those too: antivirus, firewall, email, cloud, and identity, such as Microsoft 365, Microsoft Defender, Entra ID, Fortinet, or Sophos. There are 40+ integrations, and if one is missing, we'll evaluate it.
If you decide not to sign up for TecnetSOC Agentic, your account automatically moves to the Visibility plan, which is free for up to 10 devices and renews every year. There's nothing to reinstall or reconfigure, and you keep your device inventory and visibility into what happens on them.
You receive your access by email and log in with Microsoft SSO (single sign-on) or with email and password. You install a lightweight TecnetSOC sensor on each computer, server, or virtual machine running Windows, macOS, or Linux. Everything else runs in the cloud, and your information stays in your own isolated environment. You see data in your portal the same day.
To go deeper, read What is an agentic SOC? and follow the TecnetSOC updates.